Team

Security Expert Team

Security is our craft and our passion. Our team holds offensive security certifications such as OSCP, CRTO and CEH, and brings years of hands-on IT experience, from web development and system operations to project management.
Experts
Adam Baneth
01 / 07

Adam Baneth

CEO and information security consultant, ethical hacker, IT security expert | CISA®

Specialties

Firewalls and perimeter protection, content filtering solutions, ISO standards and IT compliance, smartphone and tablet security in the enterprise
Adam Baneth is an expert in enterprise IT systems and one of the founders of Whiteshield. Before the company was founded in 2011, he spent nearly 10 years as a project manager and consultant at multinational IT companies such as Compaq, Hewlett-Packard and Epicor Software, working on a number of Hungarian and international projects. Adam graduated in finance and information systems from the University of Szeged and holds an MSc in IT Management from CEU Business School. He is a Certified Ethical Hacker, qualified at Kürt Academy.
Barna Szeghy
02 / 07

Barna Szeghy

Technical director, project manager, ethical hacker, IT security expert | CISA®

Specialties

Design and implementation flaws in web applications, database discovery and data extraction techniques, client-side JavaScript, SQL and code injection, passwords and password hashes, Python and Bash scripting
Barna Szeghy specialises in vulnerabilities of complex web applications. With more than 15 years of experience in web development and IT operations, he is at the core of our team – no surprise, since hardly any solution today comes without a web interface, whether for presentation or administration. Beyond digging through client-side JavaScript, his favourite areas are remote database discovery and the weaknesses of iOS applications, which are increasingly common in the enterprise. Barna graduated as a programmer from István Széchenyi College in Győr and obtained his Certified Ethical Hacker qualification at Kürt Academy.
Gábor Szécsi
03 / 07

Gábor Szécsi

Web application developer, ethical hacker, IT security expert | CEH | OSCP®

Specialties

Web application and internal network assessments, red team projects
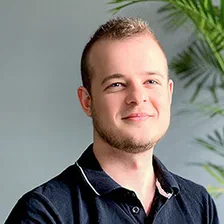
Gábor Szécsi has more than 9 years of experience in designing and developing web applications. His broad background means he not only identifies individual vulnerabilities but also works effectively with development teams to raise the security of the systems under test. He also has several years of experience in internal network assessments and red team projects. To date, he has taken part in more than 150 IT security projects across a wide range of technologies.
Kristóf Szabó
04 / 07

Kristóf Szabó

Ethical hacker | OSWP | CEH® | eJPT | eWPTX | AZ-900

Specialties

Identifying logic flaws, API abuse, bypass techniques and practical exploitation in constrained environments. His work bridges web and embedded security, combining scripting, protocol analysis and low-level hardware access.
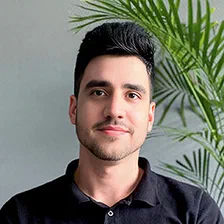
Kristóf has 7 years of experience testing the security of web applications and IT infrastructure. He has worked on international projects, both remote and on-site, including for KPMG. He adapts his methodology to each environment, whether it is a network protected by IDS, IPS or WAF systems or custom application logic. His focus areas include bypass techniques such as MIME-type confusion, token abuse and HTTP request smuggling. He has discovered vulnerabilities in IP cameras and DVR systems and has worked in depth on UART-based system access. He is currently preparing for the OSCP certification while further expanding his automation and hardware testing skills.
Attila Garamvölgyi
05 / 07

Attila Garamvölgyi

Ethical hacker | OSCP+ | CRTO | CEH | eWPTX | eMAPT | C-AI/MLPen | ISTQB CTAL-TAE

Specialties

Penetration testing and red teaming, web application and API security, security assessment of Active Directory and enterprise infrastructure, attack simulation and testing how defences can be bypassed, security testing of AI-based systems.

Attila has hands-on experience across several areas of offensive cybersecurity. He specialises in security assessments of web applications, APIs and enterprise infrastructure, and in red teaming techniques that model real attacker methods.

His OSCP+ and CRTO certifications back his knowledge of technical attack methods, Active Directory environments, privilege escalation, attacker infrastructure and bypassing defensive mechanisms. With the C-AI/MLPen certification he also specialises in uncovering the security risks of AI-based systems.

His MSc in Business Informatics and his experience across different areas of IT help him interpret technical vulnerabilities in their business context. In his work he goes beyond identifying security gaps: he puts particular emphasis on showing how exploitable they really are, what business impact they have and how they can be defended against effectively.
Fruzsina Pásztor
06 / 07

Fruzsina Pásztor

Ethical hacker

Specialties

Web application penetration testing, network and infrastructure security testing, phishing simulation, open-source intelligence (OSINT)
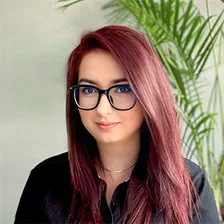
After her university studies, Fruzsina completed an IT programme at Codecool and now works as an ethical hacker. Her work focuses mainly on security testing of web applications and of network and infrastructure systems. With an attacker’s mindset, she looks for the vulnerabilities and weak points that pose a real security risk to organisations. She also takes part in phishing simulations, including creating realistic emails and websites, and works on open-source intelligence (OSINT) gathering. Continuous learning and professional growth matter to her, so alongside cybersecurity she keeps expanding her knowledge of artificial intelligence and strives to keep pace with new technologies.
Bendegúz Szeghy
07 / 07

Bendegúz Szeghy

Project manager

Specialties

B2B and B2C communication

Bendegúz has 3 years of experience coordinating complex processes, managing parallel tasks and aligning the work of different teams and departments. His strengths include effective time management, prioritising tasks and clear, goal-oriented communication across disciplines. He is currently learning mobile app development, which deepens his understanding of the technology behind the projects he coordinates.
Consultation

Security starts with a conversation.

No sales pitch – just a focused conversation about your business continuity and operational risk.